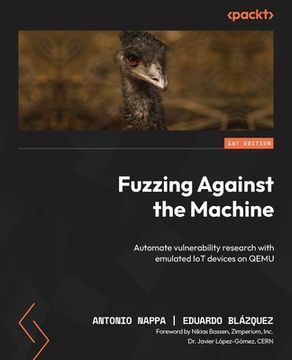
Fuzzing Against the Machine: Automate vulnerability research with emulated IoT devices on QEMU
Nappa, Antonio ; Blázquez, Eduardo
Synopsis "Fuzzing Against the Machine: Automate vulnerability research with emulated IoT devices on QEMU"
Find security flaws in any architecture effectively through emulation and fuzzing with QEMU and AFLPurchase of the print or Kindle book includes a free PDF eBookKey Features: Understand the vulnerability landscape and useful tools such as QEMU and AFLExplore use cases to find vulnerabilities and execute unknown firmwareCreate your own firmware emulation and fuzzing environment to discover vulnerabilitiesBook Description: Emulation and fuzzing are among the many techniques that can be used to improve cybersecurity; however, utilizing these efficiently can be tricky. Fuzzing Against the Machine is your hands-on guide to understanding how these powerful tools and techniques work. Using a variety of real-world use cases and practical examples, this book helps you grasp the fundamental concepts of fuzzing and emulation along with advanced vulnerability research, providing you with the tools and skills needed to find security flaws in your software.The book begins by introducing you to two open source fuzzer engines: QEMU, which allows you to run software for whatever architecture you can think of, and American fuzzy lop (AFL) and its improved version AFL++. You'll learn to combine these powerful tools to create your own emulation and fuzzing environment and then use it to discover vulnerabilities in various systems, such as iOS, Android, and Samsung's Mobile Baseband software, Shannon. After reading the introductions and setting up your environment, you'll be able to dive into whichever chapter you want, although the topics gradually become more advanced as the book progresses.By the end of this book, you'll have gained the skills, knowledge, and practice required to find flaws in any firmware by emulating and fuzzing it with QEMU and several fuzzing engines.What You Will Learn: Understand the difference between emulation and virtualizationDiscover the importance of emulation and fuzzing in cybersecurityGet to grips with fuzzing an entire operating systemDiscover how to inject a fuzzer into proprietary firmwareKnow the difference between static and dynamic fuzzingLook into combining QEMU with AFL and AFL++Explore Fuzz peripherals such as modemsFind out how to identify vulnerabilities in OpenWrtWho this book is for: This book is for security researchers, security professionals, embedded firmware engineers, and embedded software professionals. Learners interested in emulation, as well as software engineers interested in vulnerability research and exploitation, software testing, and embedded software development will also find it useful. The book assumes basic knowledge of programming (C and Python); operating systems (Linux and macOS); and the use of Linux shell, compilation, and debugging.